Uncategorized

How to Choose a CCTV System for Your Business (Not Just a Top 10 List)
Uncategorized

How to Choose a CCTV System for Your Business (Not Just a Top 10 List)

Byteway designs and installs CCTV for Australian businesses, and the way most people shop for it almost guarantees a disappointing result. They search for the best security cameras, find a top 10 list ranking gear by price or affiliate payment, and buy a kit that looks fine until the day they actually need footage and it is too blurry, too dark, or already overwritten. A CCTV system is not a product you rank; it is a system you design for your site. This guide covers how to actually choose one. The short version, before the detail: a good business CCTV system starts from what you are protecting and where, then gets the coverage, image quality, storage and retention, remote access, analytics, privacy compliance and camera security right for your site. The best system is the one designed for your premises and your risks, not the highest-rated kit on a list. Cameras are the easy part; the plan behind them is what makes footage useful when it matters. How to actually choose: the framework 1. Start with what you are protecting, and why Before looking at any camera, decide what the system is for: deterring theft, capturing usable evidence, monitoring staff safety, watching a yard or car park, meeting an insurance or compliance requirement. The purpose shapes everything, camera type, placement, quality and retention, so a system built for evidence looks different from one built mainly for deterrence. 2. Coverage and placement, as a plan The most common failure is cameras placed where convenient rather than where they matter, leaving blind spots at exactly the points that count, entries, exits, tills, loading docks, blind corners. Good CCTV starts with a coverage plan of your actual site, so every important area is covered and the cameras suit each spot. This planning, not the camera brand, is what makes a system work. 3. Image quality that can actually identify There is a big difference between footage that shows something happened and footage that identifies who did it. Resolution, lens choice and positioning determine whether you get a usable image or a blurry shape. A camera has to be specified and placed to capture identifiable detail at the distance it is actually covering, which is a design decision, not just a spec-sheet number. 4. Low-light and night performance Many incidents happen after dark, so how cameras perform in low light often matters more than their daytime specs. Consider the real lighting at each location and choose cameras that deliver usable footage in those exact conditions, because a camera that is sharp by day and useless by night fails when you most need it. 5. Storage, retention and how long footage is kept Footage is only useful if it still exists when you need it. Decide how long you need to retain recordings, sometimes weeks, sometimes longer for compliance or insurance, and size storage accordingly, whether local recording or cloud. A system that overwrites footage before you review an incident is a system that failed quietly. Retention also has a privacy dimension, covered below. 6. Remote access and alerts Being able to view your cameras from your phone or from head office, and to get alerts, turns CCTV from a passive record into an active tool. If remote monitoring matters to you, factor in secure remote access, which also raises the security considerations below. 7. Analytics and smart features, where they earn their place Modern systems can detect people or vehicles, flag motion in defined zones, and cut down false alarms. These features are genuinely useful when they fit your needs, and unnecessary cost when they do not. Choose them for real use, not novelty. We cover this in depth in our guide to AI CCTV cameras. 8. Privacy and legal compliance This is the part businesses most often get wrong, and it carries real risk. CCTV in Australia is subject to surveillance and privacy laws: you generally need appropriate signage, you must be careful about recording audio (which has stricter consent rules), you should avoid covering areas with a high expectation of privacy, and you should not overlook neighbouring properties. Businesses covered by the Privacy Act also have obligations for the footage they hold. We cover this fully in our guide to CCTV and privacy law. Getting it right protects you as much as the cameras do. 9. The security of the cameras themselves This one is routinely ignored. CCTV cameras are network-connected devices, and poorly secured cameras have been hijacked, used to spy, or used as a way into business networks. Your cameras need to sit behind proper network security, changed default passwords, secure configuration, and ideally segmented from your main network, so the system protecting your business does not become a way into it. This is where CCTV and cyber security meet. 10. Support and who maintains it A camera that has been offline for a month is discovered the day you need its footage. Consider who installs, monitors and maintains the system, and how you will know if a camera fails. Ongoing support is what keeps the whole system actually working when it counts. The cheap-kit-off-the-shelf trap A boxed CCTV kit from an electronics store is tempting on price, and it is where many businesses go wrong. The cameras may be fine; the problem is that nobody designed the coverage, specified the quality for the distances involved, planned the retention, secured the devices or handled the privacy obligations. You end up with cameras that record, and a system that does not deliver when it matters. The value is in the design and setup, not the box. Byteway Expert Insight Almost every business that calls us disappointed with CCTV has the same story: they bought cameras, not a system. The footage exists, but the one angle they needed is a blind spot, or the image is too soft to identify anyone, or it was overwritten before they looked, or, occasionally, the cameras were sitting unsecured on the network as a genuine
How to Actually Choose a Managed IT Provider in Melbourne
Uncategorized

How to Actually Choose a Managed IT Provider in Melbourne (Not Another Top 10 List)

Byteway is a Melbourne managed IT provider, so we will be upfront: this is not a list ranking us at number one. Search for the best IT provider in Melbourne and you get exactly that, directories and “top 10” pages ranked by advertising spend and SEO, not by which provider actually fits your business. Those lists cannot tell you who is right for you, because the right provider depends on your business, not on who paid to rank. This guide gives you a way to actually choose one, by what you need. The short version, before the detail: the right Melbourne managed IT provider is the one that fits your size, systems and industry, responds fast with guaranteed times, takes security seriously, is genuinely local when you need onsite help, lets you keep control of your own systems, and can grow with you. Choose by matching a provider to your real needs and testing how they answer the hard questions, not by trusting a ranking. A provider that fits scores better for you than any “number one” ever could. How to actually choose: the framework Work through these, judging each provider against your business. 1. Start with what you actually need Before contacting anyone, get clear on your situation. How many staff and sites, what systems do you run, do you have any in-house IT, what industry obligations apply, and what is actually going wrong today. A ten-person firm with one office needs something different from a fifty-person business across three sites. Knowing your needs first stops you being sold a package that suits the provider more than you. 2. Proactive management, not reactive break-fix “Managed IT” should mean a provider who monitors your systems and prevents problems, not one who waits for you to call when something breaks. Ask what they do when nothing is broken. If the honest answer is “nothing,” you are buying break-fix with a nicer name. Our guide on IT support versus managed IT explains the difference that matters here. 3. Guaranteed response times and a clear agreement When your systems go down, response speed is all that matters. Ask for guaranteed response and resolution times, and make sure the service agreement is specific about what is covered. Vague promises are not commitments. Our onboarding and SLA checklist covers exactly what to demand before signing. 4. Real security capability Your network and your security are one job. A provider weak on cyber security leaves your most important gap open, and in a year of record data breaches that is not acceptable. Ask what they do about multi-factor authentication, backups, patching, monitoring and breach response. 5. Genuinely local, when local matters This is where a Melbourne provider earns its place over a faceless national helpdesk. Local matters when you need someone onsite, quickly, to deal with hardware, a network problem or a new office fit-out, and when you want a provider who understands Melbourne business and can actually turn up. Ask honestly how they handle onsite work, where their people are, and how fast they can be at your door. “Local” should mean real presence, not a local phone number routing to a distant queue. 6. Track record with businesses like yours Ask for references, and specifically for clients similar to you in size and industry. How long do they keep clients? A provider who retains happy clients for years is telling you something a sales pitch cannot. One who cannot point to comparable local clients is a bigger risk. 7. Clear scope, transparent pricing, and no lock-in Know exactly what is included and what costs extra, so the invoice never surprises you, and check the exit terms. Do you own your data, documentation and licences, and how would a handover work if you left? A confident provider is comfortable with a fair exit. One who makes leaving hard is planning for you to want to. 8. Can they handle your whole environment Your IT does not live in isolation; it connects to your internet and your phones. A provider who can manage the network, connectivity and phones together gives you one accountable partner instead of separate suppliers blaming each other when something goes wrong. For many businesses that joined-up model is a real advantage worth weighing. 9. Communication and fit If you cannot get a clear, jargon-free answer during the sales process, it will not improve after you sign. You want a provider who communicates like a partner and whom your team will actually work well with. The sales experience is the best version you will get, so judge it. How to run the selection Shortlist two or three genuine options, not ten. Put each through the questions above, weighted for your business, ask the uncomfortable ones early, guaranteed response times, security, onsite capability, exit terms, and check references. The provider that fits your needs and answers straight is the right choice, whatever any list says. If you are currently with the wrong provider, our guide on switching managed IT providers in Melbourne covers doing it cleanly. What “local” actually buys you in Melbourne? Local is worth being specific about, because it is easy to overclaim. A genuinely local Melbourne provider can get someone onsite when a problem needs hands on hardware, understands the businesses and conditions here, and gives you a real relationship rather than a ticket number in a distant queue. That does not mean a national provider can never serve you well, but if onsite response and local understanding matter to your business, a real local presence is a legitimate and important factor, not marketing. Byteway Expert Insight The businesses that choose well almost never do it from a list. They work out what they actually need, shortlist a couple of providers, and then ask the questions the sales process would rather avoid: what are your guaranteed response times, what do you do about security, can you be onsite when I need you, and what happens if I want to leave.

How to Actually Compare Video Conferencing Providers for Business (Not a Top 10 List)
Uncategorized

How to Actually Compare Video Conferencing Providers for Business (Not a Top 10 List)

Byteway helps Australian businesses choose and set up the technology that fits them, and video conferencing is a category where the usual advice fails badly. Search for the best platform and you get a top 10 list ranking the same handful of names by popularity, or by who paid to be there. That tells you nothing about which one is right for your business, because the right one depends entirely on how you work. This guide gives you a way to actually compare providers, against your needs, so you choose well instead of following a list. The short version, before the detail: the best video conferencing provider is the one that fits how your business actually uses it, integrates with what you already run, and meets your security and budget needs, not the one at the top of a list. Compare on your real usage, your existing tools (you may already own a capable platform), reliability, security and compliance, ease of adoption, total cost and support. A platform that scores well against your needs beats the “number one pick” every time. How to actually compare: the framework? Work through these, scoring each provider against your business rather than against each other in the abstract. 1. Start with how you actually use video conferencing Before looking at any platform, map your real usage. How many people are in a typical meeting, and the largest ones? Are meetings mostly internal, or client- and public-facing? Do you run webinars or training? How often, and from where? A business doing quick internal standups needs something very different from one running large external client presentations. Your usage pattern is the single biggest factor, and it is the one the lists never ask about. 2. Integration with what you already run The best platform for you usually plugs cleanly into your existing tools: your email and calendar, your file storage, your phone system, your CRM. A platform that fits your stack saves friction every day; one that fights it creates daily annoyance. If you already run Microsoft 365 or Google Workspace, the video tool built into it may integrate better than anything you would buy separately, which leads to the next point. 3. You may already own a capable platform This is the most overlooked money-saver in the category. If your business runs Microsoft 365, you very likely already have Microsoft Teams included. If you run Google Workspace, you have Google Meet. Before paying for a separate platform, check whether the one you already own does what you need, because paying twice for video conferencing is common and avoidable. We cover getting value from your existing licences in our Microsoft 365 licensing guide. 4. Reliability and quality A video platform that drops calls, lags or cannot handle your largest meetings is a daily liability, however good its feature list. Consider call quality, how it performs on your actual internet connection, and whether it holds up at the meeting sizes you run. Reliability matters more than any single flashy feature, because an unreliable tool simply will not get used. 5. Security and compliance How much this matters depends on your business, but for anyone handling confidential or regulated information it is decisive. Look at encryption, where data and recordings are stored, access controls like waiting rooms and meeting locks, and how recording and consent are handled. For regulated sectors such as legal, medical and finance, this becomes a primary filter, not an afterthought. We go deep on this for law firms in our piece on what actually needs to be secure in video conferencing, and it connects to your broader cyber security. 6. Ease of use and adoption A platform staff and clients find awkward will not get used, no matter how capable it is. Consider how easily your team will adopt it and how simple it is for an external client to join without installing or fighting software. The most secure, feature-rich platform is worthless if people avoid it, so weigh real-world usability heavily. 7. Recording, retention and transcription If you record meetings, think through where recordings are stored, for how long, who can access them, and the consent rules, which vary by state and treat a transcript like a recording. For some businesses this is a minor convenience; for regulated ones it is a compliance question that can rule platforms in or out. 8. Total cost, honestly Compare the real cost, not the headline per-user price: what is included versus charged as add-ons, whether you already own a capable tool, and the cost of the licences at the tier you actually need. Sometimes the right answer costs nothing extra because it is already in your subscription. Sometimes a paid platform is worth it for specific needs. The point is to compare total cost against fit, not to chase the cheapest or the most feature-packed. 9. Support and management When a call fails before an important client meeting, who fixes it? A platform set up and managed properly, integrated with your systems and supported when it breaks, is worth more than a marginally better feature set with nobody behind it. Consider how it will be supported, especially if you lack in-house IT. How to run the comparison? Score two or three genuine options against these factors, weighted for your business, and trial them with real meetings before committing. The winner is whichever fits your usage, integrates with your tools, meets your security needs and does not cost more than it should, not whichever a list crowned. Nine times out of ten this produces a clearer, cheaper and better-fitting answer than any ranking. Byteway Expert Insight The two things we see most often are businesses paying for a separate video platform while a perfectly good one sits unused inside their Microsoft 365 subscription, and businesses that chose from a list and ended up with a tool that fights their existing systems every day. Both come from asking “what’s the best platform” instead of “what fits how

Uncategorized

Before You Sign With a New IT Provider: The Onboarding and SLA Checklist Most Businesses Skip

Byteway onboards Australian businesses onto managed IT, and we can tell you the two things that decide whether the relationship works are settled before anyone fixes a single problem: what is written in the service level agreement, and how the onboarding is run. Most businesses skip both. They compare monthly prices, sign, and discover the gaps later, when something breaks or a surprise bill lands. This checklist covers what to check in the SLA and the onboarding before you sign, so you choose with your eyes open. The short version, so you have it up front: before signing an IT provider, your SLA should spell out guaranteed response and resolution times by priority, coverage hours, exactly what is in and out of scope, security and backup commitments, reporting, an escalation path, and clean exit terms. The onboarding should include a proper audit of your systems, documentation you own, a secure access handover, a baseline security review and a clear transition plan. If a provider is vague on these, that vagueness is the product you are buying. Why the SLA and onboarding matter more than the price? The monthly figure is the easiest thing to compare and the least important thing to get right. The SLA is where the actual promises live, how fast they respond, what they will and will not do, what happens when things go wrong. The onboarding is where the relationship is either set up to succeed or quietly undermined, because a provider who never properly learns and documents your environment cannot support it well. Skip these and you are signing on trust and a headline number, which is exactly how businesses end up unhappy and stuck. The SLA checklist: what must be in the agreement Run any proposed agreement against this list before signing. Guaranteed response and resolution times, by priority. Not “we’ll get to it,” but defined times, and different ones for a full outage versus a minor issue. Response time (when they acknowledge) and resolution or restoration expectations should both be there. Vague timing is the most common gap. Coverage hours, and after-hours. When is support available, and what happens outside those hours. If your business runs evenings or weekends, confirm you are covered then, and what it costs. Exactly what is in scope, and what is out. The single biggest source of surprise bills. The agreement should list what is included in your monthly fee and what is charged separately, projects, new hardware, after-hours call-outs, so nothing is a shock later. Security inclusions. What the provider actually does for cyber security: multi-factor authentication, patching, monitoring, endpoint protection. Security should be part of the service, not a vague assurance or a costly afterthought. Backup and recovery commitments. How your data is backed up, how often, and, in plain terms, how quickly you would be back up and how much data you could lose in a worst case. If those backup and recovery expectations are not written down, they are not commitments. Reporting and reviews. How you will see what the provider is doing, ticket reports, regular reviews, so the service is visible and accountable rather than a black box. Escalation path and named contacts. Who you call, and what happens if the first response is not enough. A real escalation path, and ideally a named contact or team, beats a generic queue. Exit and offboarding terms. What happens if you leave, do you own your data, documentation and licences, and how is a handover managed. A fair exit clause is a sign of a confident provider. Its absence is a warning. Pricing clarity and what triggers extra cost. Beyond the monthly fee, know exactly what generates additional charges, so the invoice never surprises you. The onboarding checklist: what good onboarding looks like The first weeks tell you what the relationship will be. Good onboarding includes: A proper audit of your environment. Before managing your IT, a good provider surveys it, hardware, software, network, security, licences, so they actually understand what they are supporting. A provider who starts without this is guessing. Documentation you own. Your systems, configurations and passwords should be documented, and that documentation should be yours, not locked in the provider’s head. This is what stops you being trapped later. A secure access handover. Access should be transferred securely, with old credentials rotated, especially if you are moving from a previous provider or staff member. This is a security-critical step often done carelessly. A baseline security review. Early on, the provider should check the fundamentals, MFA, backups, patching, access, and flag what needs fixing. Onboarding is the natural moment to close obvious gaps. A clear transition plan and timeline. You should know what happens when, who is doing it, and when you will be fully up and running, with no long dead period where nobody owns your IT. A named team and a kickoff. You should know who you are working with and have a proper start, not be handed a portal login and left to it. Red flags before you sign Byteway Expert Insight The businesses that come to us unhappy with a previous provider almost never had a dramatic falling-out. They had a vague agreement and a rushed onboarding, and the small gaps compounded, a response that was slower than assumed, a project that cost more than expected, a backup nobody had confirmed, documentation nobody could find when they wanted to leave. None of it was in writing, so none of it could be held to. Our advice before signing anyone, us included, is to make the boring parts explicit: get the response times, the scope, the security, the backups and the exit written down, and insist on a real onboarding that audits and documents your environment. It is not the exciting part of choosing a provider, and it is the part that determines whether you are happy in two years. How Byteway helps? Sign with your eyes open The right IT provider makes the promises specific and the

ASD Issued a Critical Alert on 9 July for Web CMS Exploitation. Three Questions to Ask Your IT Provider This Week.
Uncategorized

ASD Issued a Critical Alert on 9 July for Web CMS Exploitation. Three Questions to Ask Your IT Provider This Week.

If someone looks after your website, firewall and IT, you probably assume they are already watching for critical security alerts. But for many small businesses, that responsibility is split between a web developer, hosting provider, marketing team and IT provider which means nobody is actually checking everything. That matters right now. On 9 July 2026, the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) issued a Critical alert about a large-scale campaign targeting vulnerable website content management systems (CMS) and plugins. Just three weeks earlier, ACSC had issued another Critical alert involving Fortinet firewalls and VPN gateways. The two incidents are different, but they point to the same problem: businesses need someone actively checking whether their internet-facing systems are patched, secure and already compromised. This guide explains what the alerts mean, what you should check, and how Byteway can help. What was the ACSC Critical alert in July 2026? On 9 July 2026, ASD’s ACSC published a Critical alert warning about a large-scale global campaign exploiting known vulnerabilities in website CMS platforms and plugins. The campaign includes Australian businesses, with many small and medium-sized businesses already affected. The attack method is relatively straightforward. Attackers automatically scan internet-facing websites looking for software with known vulnerabilities. When they find an unpatched system, they exploit it and can install a webshell — code that gives them persistent remote access to the web server. The affected products include around 17 CMS platforms and plugins, with WordPress plugins representing a major attack vector. Other products mentioned include Craft CMS, Joomla JCE, MaxSite CMS and MetInfo CMS. Once attackers gain access, the website can become more than just a defaced webpage. They may be able to: That last point is particularly important. Your website may be a marketing asset to you, but an attacker can see it as an entry point into your business. The biggest problem isn’t a zero-day There is an uncomfortable detail behind the July alert. The vulnerabilities involved already have patches available. This means businesses are not necessarily being compromised because attackers have discovered an unknown vulnerability. Many are being compromised because known vulnerabilities have not been fixed. The referenced CVEs range from recent disclosures back to vulnerabilities dating as far back as 2020. That creates a simple security lesson: Knowing about a vulnerability is not the same as fixing it. ASD’s ACSC has also noted that the speed and scale of scanning and exploitation may indicate the use of AI-assisted tooling, potentially reducing the time businesses have between a vulnerability being publicly known and attackers attempting to exploit it. For a small business, waiting until someone notices something is wrong is no longer a sensible security strategy. What about the Fortinet Critical alert? The website campaign wasn’t the only recent warning. On 18 June 2026, ASD’s ACSC published an alert concerning a widespread campaign targeting Fortinet firewalls and VPN gateways. The alert was subsequently reissued on 22 June following further analysis from Fortinet. The important distinction is that this is not simply a patching problem. The campaign involved compromised administrator and VPN credentials being reused to access FortiGate devices. That means a business could have a fully patched firewall and still have a problem if exposed credentials have never been changed. For organisations using Fortinet equipment, the practical checks include: Patching and credential rotation are two different security tasks. Fixing the software does not automatically invalidate credentials that may already have been compromised. What should you ask your IT provider this week? You don’t need to understand CVEs, webshells or firewall firmware to have a useful conversation with your IT provider. Ask these three questions. 1. Is our website fully patched? Don’t settle for: “It updates automatically.” Ask: When was it last checked and verified? Your provider should be able to confirm that the CMS, plugins and other internet-facing components are running supported versions and that updates have actually been applied. 2. Have you checked whether we’ve already been compromised? This is arguably the most important question. Patching closes the vulnerability. It does not remove an attacker who may already have access. If a webshell was installed before the patch, it may remain on the server. A proper assessment should therefore look for indicators such as: If evidence of compromise is found, the system should be treated as compromised and investigated rather than simply patched and returned to normal. 3. If we use Fortinet, have all administrator and VPN credentials been rotated? Don’t just ask whether the firewall is patched. Ask whether the relevant credentials have been changed and secured, whether MFA is enforced and whether authentication logs have been reviewed. A clear answer should include when these checks were completed. What if nobody manages your website? This is more common than many business owners realise. Your website might have been built several years ago by a web agency. The agency no longer manages it. Your hosting company manages the server but not the CMS. Your marketing person manages content but not security. Your IT provider manages laptops and Microsoft 365 but has never been given website access. Everyone thinks someone else is responsible. That creates a security gap. If there is no clearly assigned owner, start with these steps: 1. Identify who has access Find out who controls: 2. Update the CMS and plugins Make sure the CMS and all installed plugins are supported and patched. Remove plugins you no longer use rather than leaving unnecessary software installed. 3. Check for existing compromise Don’t assume that updating the software means the site is clean. Have someone appropriately qualified inspect the website and server for signs of unauthorised access. 4. Secure administrator accounts Enable MFA wherever available and eliminate unnecessary administrator accounts. 5. Check your backups Make sure you have a usable backup — and, more importantly, that somebody has tested restoring it. A backup that has never been restored is an assumption, not a recovery strategy. 6. Assign ongoing responsibility Someone should own website security going forward. Not

The 13 Australian Privacy Principles, Translated for a Five-Person Real Estate Office
Uncategorized

The 13 Australian Privacy Principles, Translated for a Five-Person Real Estate Office

If the AML/CTF reforms have just brought your firm under the Privacy Act, you have probably been handed a document listing 13 Australian Privacy Principles (APPs) written in the kind of language that assumes you employ a compliance team. You don’t. You might have four or five people in the office, with one person handling bookkeeping, another managing clients and everyone wearing multiple hats. So here are the 13 Australian Privacy Principles explained in plain English, with what each one actually means for a small Australian office handling client identity documents, tenancy applications, financial information and property files. The important thing is not memorising all 13. It is understanding what you actually need to change in your day-to-day operations. What Are the Australian Privacy Principles? The Australian Privacy Principles are 13 legally binding principles contained in Schedule 1 of the Privacy Act 1988. They govern how organisations covered by the Privacy Act collect, use, store, secure, disclose and provide access to personal information. For a small business, think of them as rules covering the entire life of someone’s information: Collect it → tell them why → use it properly → keep it secure → let them access it → correct it → delete it when you no longer need it. Personal information can include anything that identifies, or could reasonably identify, an individual. For a real estate or property business, that might include: The 13 principles are easier to understand when grouped into five practical areas. Part 1: Being Open About What You Do APP 1: Be Open and Transparent About Personal Information APP 1 requires organisations to manage personal information openly and transparently. In practical terms, you need a clear, current privacy policy explaining things such as: Your privacy policy should be freely available and easy for people to find, typically through your website. What this means for a small office A generic privacy policy downloaded several years ago and forgotten about is unlikely to be enough. Your policy should reflect what your business actually does. If your office collects identity documents, stores client information in cloud software, uses external providers and communicates with clients electronically, your privacy documentation should reflect that reality. APP 2: Allow Anonymity or Pseudonymity Where Practical APP 2 says individuals should generally have the option of dealing with an organisation anonymously or using a pseudonym where this is lawful and practical. For many professional and property businesses, this will have limited practical application. You cannot realistically complete a tenancy application, verify a client or perform certain AML/CTF requirements without knowing who the person is. So while APP 2 is still part of the framework, it is not usually where a small property or professional office will spend most of its time. Part 2: Collecting Personal Information APP 3: Only Collect What You Actually Need APP 3 is about limiting the personal information you collect. You should only collect information that is reasonably necessary for your functions or activities. Sensitive information has additional requirements. What this means for a small office This is where businesses can easily collect more information than they actually need. For example, if you need evidence of income for a particular process, automatically requesting an entire collection of financial documents may result in more personal information being collected than necessary. The practical question is: Do we actually need this information to perform the task? If the answer is no, don’t collect it simply because it might be useful later. APP 4: Deal Properly With Unsolicited Information APP 4 deals with personal information that your business receives without asking for it. If someone sends you information you did not request, you need to consider whether you could have collected it lawfully. If you could not have collected it lawfully, you generally need to destroy or de-identify it as required. What this means for a small office Think about a client or applicant who emails a large folder of documents “just in case.” You didn’t ask for them. You don’t need them. Don’t automatically save them forever. Unnecessary information sitting in your inbox or shared drive is still information your business has to protect. APP 5: Tell People What You Are Collecting and Why APP 5 requires you to provide appropriate notification when collecting personal information. People should understand: This is commonly handled through a collection notice. Privacy policy vs collection notice These are not the same thing. Your privacy policy explains your broader information-handling practices. Your collection notice appears at or before the point where you collect information. For a small property or professional business, that may mean including appropriate wording in: A business can have a privacy policy and still fail to properly address collection notices. Part 3: Using and Sharing Personal Information APP 6: Use Information for the Right Purpose APP 6 governs how you use and disclose personal information. Generally, information should be used or disclosed for the purpose it was collected for, unless consent or another permitted exception applies. A simple example If you collect identity documents for identity verification or AML/CTF purposes, that does not automatically mean you can use those documents for unrelated marketing. The key question is: Why did we collect this information in the first place? The answer should guide how you use it. APP 7: Be Careful With Direct Marketing APP 7 deals with using personal information for direct marketing. Depending on the circumstances, you may need consent or another lawful basis, and individuals generally need a straightforward way to opt out. For property businesses, this can cover activities such as: If someone has opted out, your systems need to respect that decision. A marketing database that continues sending emails after an unsubscribe request is more than a marketing inconvenience—it can become a privacy issue. APP 8: Take Care With Overseas Disclosures APP 8 deals with cross-border disclosure of personal information. This is increasingly important because many businesses rely on cloud-based software. Your CRM, document management platform, email service or other technology

business phone systems (on-premise & hosted_cloud pbx) sunshine coast
Uncategorized

Business Phone Systems Sunshine Coast: VoIP & Hosted PBX for Australian Businesses

The Sunshine Coast business landscape is changing quickly. From the Maroochydore CBD and professional services to healthcare, technology, tourism and multi-location businesses, organisations need phone systems that can keep up with mobile teams, growing staff numbers and customers calling from anywhere. Byteway provides business phone systems on the Sunshine Coast, combining hosted PBX, VoIP, business connectivity, managed IT and cyber security into a communications setup built around your business. A Phone System That Works Beyond the Office Your team may be working from the office, home, another location or on the road. Byteway’s business phone systems can bring those users into one communication platform with: The result is a more consistent way for customers to reach your business, regardless of where your team is working. Built for the Way Sunshine Coast Businesses Are Growing Professional Services Keep sales, service and administration teams connected with call routing, CRM integration, business numbers and call management. Healthcare Support patient bookings and remote communication with structured call handling, controlled access and appropriate security configuration. Technology Businesses Add users, locations and calling capabilities without having to redesign the entire phone system as your business grows. Tourism & Hospitality Handle busy periods with call queues, automated greetings, forwarding and after-hours call management. Multi-Location Businesses Bring different offices or sites into one phone environment instead of managing separate systems at every location. Cloud PBX Without the Hardware Headache For many growing Sunshine Coast businesses, hosted PBX provides a practical alternative to maintaining a traditional phone system on-site. Users can be managed centrally, remote employees can be supported and new extensions can be added as the business changes. However, hosted PBX isn’t automatically the right choice for everyone. If your business already has substantial phone infrastructure, operates from a single location or has specific technical requirements, on-premise or hybrid systems may still make sense. Byteway looks at your existing setup before recommending a migration. Your Internet Connection Is Part of Your Phone System A great phone platform won’t fix a poor business connection. VoIP calls rely on the network carrying the voice traffic, so Byteway considers: Phone system + Internet connection + Network + Security Depending on your location and requirements, Byteway can support your phone system with business NBN & dedicated fibre and managed network services. This gives you one team responsible for the technology behind your business communications. Make It Easier for Customers to Reach You Missed calls can mean missed enquiries. Byteway can configure automated call flows that help customers reach the right person without having to call multiple numbers. For example: Customer calls → Business greeting → Department selection → Call queue → Staff member You can also configure different routing for: One Byteway Partner for Communications & IT Your business phone system doesn’t need to sit with one provider, your internet with another and your IT with someone else. Byteway can bring these services together: Business Phone Systems↓Business Internet & Fibre↓Managed IT↓Cyber Security↓Cloud & Backup Explore Byteway’s managed IT services, cyber security and cloud backup to build a broader technology environment around your phone system. Which Phone System Is Right for Your Sunshine Coast Business? Don’t choose a phone system based on features alone. Byteway looks at: From there, Byteway can recommend hosted PBX, VoIP, on-premise or hybrid communications based on what your business actually needs. Upgrade Your Sunshine Coast Business Phone System Whether you’re opening a new office in Maroochydore, expanding across the Sunshine Coast, supporting remote employees or replacing an ageing phone system, Byteway can help. Get a free quote within 24 hours. Talk to Byteway about a business phone system designed around your users, locations and growth. Frequently Asked Questions How much does a business phone system cost on the Sunshine Coast? Business phone system costs vary depending on the number of users, features, hardware, calling requirements and connectivity. Byteway can assess your requirements and provide a solution based on your business rather than putting you into a standard package you don’t need. Can Byteway connect multiple Sunshine Coast offices? Yes. A hosted PBX can connect multiple offices under one phone system, allowing teams to transfer calls and manage users centrally. Byteway can design the setup around your locations, users and existing connectivity. Can employees use the business phone system from home? Yes. Supported hosted PBX platforms can provide desktop and mobile calling, allowing authorised employees to remain connected while working remotely. Is VoIP suitable for Sunshine Coast businesses? VoIP can be suitable for businesses with a reliable, appropriately configured internet connection. Byteway checks the underlying connectivity as part of the phone-system assessment rather than treating VoIP as a standalone service. Can I keep my existing business number? In many cases, yes. Existing business numbers can often be ported when moving to another provider. Byteway can help assess your current numbers and plan the transition. Can I add new employees without replacing my phone system? With a hosted PBX, new users can generally be added through the system’s administration platform without installing a new PBX for every change. This can make cloud phone systems particularly useful for growing Sunshine Coast businesses. Can Byteway manage our phone system and IT? Yes. Byteway can manage your business phone system alongside connectivity, managed IT, cyber security and cloud services. This means your communications infrastructure can be managed as part of your wider technology environment.

AML-CTF Reforms
Uncategorized

AML/CTF Reforms Just Pulled 100,000+ Legal and Property Firms Into the Privacy Act. Here’s What Changes.

If you run a small law practice, accounting firm, conveyancing business or real estate agency, you may have spent years assuming the Privacy Act did not apply to you. Under the small business exemption, businesses with turnover below $3 million generally sat outside it. That changed on 1 July 2026 for firms captured by the AML/CTF Tranche 2 reforms. The trigger was not a standalone privacy reform. The change came from the expansion of Australia’s Anti-Money Laundering and Counter-Terrorism Financing regime, which brought a range of professional and property-related businesses into the definition of reporting entities. For affected firms, this also changes how the Privacy Act applies to personal information handled in connection with their AML/CTF obligations. The first major deadline was 29 July 2026, when affected businesses were required to enroll with AUSTRAC. If your firm is affected, this is not simply a compliance paperwork exercise. It has direct implications for how you collect, store, secure and respond to breaches involving client information. Here’s what changed, who is affected and what your business needs to have in place. What Happened on 1 July 2026? Two important changes happened at the same time, and the second is the one many small firms have overlooked. First, AML/CTF Tranche 2 took effect. The Anti-Money Laundering and Counter-Terrorism Financing Amendment Act 2024 extended Australia’s AML/CTF regime beyond traditional financial institutions to a range of professional and property-related businesses. Lawyers, accountants, conveyancers, real estate professionals, trust and company service providers, and dealers in precious metals and stones can now fall within the regime when they provide a designated service. Second, becoming an AML/CTF reporting entity can affect the Privacy Act small business exemption. The Privacy Act contains an exception to the small business exemption for reporting entities under the AML/CTF Act. That means a business cannot simply rely on its turnover being below $3 million if it has become a reporting entity. For affected firms, the Privacy Act therefore applies to personal information handled for the purposes of, or in connection with, their AML/CTF obligations, regardless of turnover. That distinction matters. The change does not necessarily mean every piece of information held by every affected business is automatically treated in exactly the same way. But for most firms, separating AML/CTF-related information from ordinary client information can be difficult in practice. Who Is Actually Affected? The important question is not simply what your job title is. It is whether your business provides a designated service under the AML/CTF framework. The reforms broadly bring the following professional and property-related businesses into scope where they provide designated services: If you are unsure whether your business is captured, check your eligibility rather than assuming the small business exemption still protects you. For real estate businesses and other affected firms, enrolment with AUSTRAC was due by 29 July 2026 for businesses providing designated services from 1 July. Importantly, enrolment is not what creates the underlying obligations; businesses captured by the reforms became subject to the relevant requirements from 1 July. What Does the Privacy Act Now Require? The change is more specific than simply saying that every small business has suddenly become fully subject to the Privacy Act. The exemption falls away for personal information you handle for the purposes of, or in connection with, your AML/CTF obligations. That can include customer due diligence information, identity verification information and records maintained to demonstrate compliance. For affected information, businesses need to consider requirements including: For many small firms, the practical challenge is separating AML/CTF-related client information from everything else. That is why bringing the broader practice up to appropriate privacy and security standards can be a more practical approach than trying to maintain complicated boundaries between different categories of client information. The Notifiable Data Breaches Scheme Now Matters For affected firms, one of the biggest practical changes is the Notifiable Data Breaches (NDB) scheme. If personal information is lost or accessed without authorisation and the incident is likely to result in serious harm, the business may need to assess the incident and notify the OAIC and affected individuals. That creates a very different operational requirement for a small practice that has never previously needed formal breach processes. You need to be able to: A written breach response plan is therefore only part of the solution. You also need enough visibility across your systems to know that something has happened in the first place. That is particularly important for firms holding identity documents, financial information, property records and other sensitive client data. Why This Is More Than a Compliance Problem This is where the legal and IT sides of the change meet. A lawyer or compliance consultant can help you understand your obligations and develop the appropriate policies and procedures. But a policy cannot secure your Microsoft 365 account. It cannot enforce multi-factor authentication. It cannot restrict access to sensitive client folders. It cannot patch an outdated device. And it cannot tell you that someone has accessed a system unexpectedly. That is why the technical controls behind the compliance program matter. For a small firm holding sensitive client information, reasonable security measures can include: These controls also align closely with the Essential Eight, which provides a practical cybersecurity baseline for Australian organisations. For businesses trying to demonstrate that they have taken reasonable steps to protect sensitive information, having appropriate technical controls in place can provide a much stronger position than relying on policies alone. What Are the Penalties? Both the Privacy Act and AML/CTF framework carry significant penalties, although the regimes are separate. Under the Privacy Act, serious or repeated interferences with privacy can attract substantial penalties, including amounts of up to $50 million, three times the benefit obtained, or 30% of adjusted turnover, whichever is highest, depending on the circumstances. The OAIC can also issue infringement notices for certain lower-level failures. The AML/CTF framework carries its own civil penalty provisions, with corporate penalties potentially reaching tens of millions of dollars for serious contraventions. For a small business, however, the

Outsourced IT Support Cost in Australia What Small Businesses Actually Pay in 2026 (1)
Uncategorized

Outsourced IT Support Cost in Australia: What Small Businesses Actually Pay in 2026

If you are comparing IT support providers, getting a straight answer on price can be surprisingly difficult. Most providers will tell you that “it depends” and technically, it does. Your team size, number of devices, security requirements, support hours, locations and existing systems can all affect the final cost. But you should still be able to understand the numbers before you book a sales call. In 2026, outsourced IT support for Australian small businesses generally costs around $100 to $250 per user per month for managed services. Ad-hoc IT support typically ranges from $150 to $250 per hour, while hiring one in-house IT professional can cost $115,000 to $175,000 per year once salary and employment costs are taken into account. So which option makes the most financial sense for a growing Australian business? This guide breaks down the typical cost of outsourced IT support, compares it with hiring in-house, explains what affects your monthly bill and shows what to look for when comparing IT providers. How much does Outsourced IT support cost in Australia? Most managed IT providers in Australia use a per-user, per-month pricing model. This makes budgeting easier because your IT costs scale with the size of your team. Typical 2026 pricing looks like this: Tier Cost (per user / month) What you get Basic $89 to $150 Helpdesk, monitoring, patching, endpoint protection Standard (most common) $140 to $250 The above, plus stronger security, unlimited support, proactive management Comprehensive $250 to $349 The above, plus 24/7 support, compliance, strategy For example, a business with 20 employees could expect to spend approximately $1,780 to $2,980 per month on a standard managed IT package, depending on what is included. The important point is that price alone does not tell you whether an IT support package represents good value. One provider might charge $120 per user but exclude backup, cybersecurity tools and after-hours support. Another might charge $180 but include those services as part of the monthly fee. That is why Byteway recommends comparing scope, coverage and included services, rather than simply choosing the lowest price per user. What Does Managed IT Support Usually Include? Depending on the provider and package, managed IT support can include: Before signing a contract, ask your provider to clearly separate what is included, charged separately and excluded. Outsourced IT support vs hiring in-house: the real cost comparison This is often the biggest question for a growing business. At first glance, hiring an employee can appear cheaper because you have someone sitting inside the business every day. But salary is only one part of the cost. A single in-house IT professional can cost approximately $115,000 to $175,000 per year once salary, superannuation, leave, recruitment, training, software and other employment costs are considered. And that investment gives you one person. An outsourced IT provider gives you access to a team with different areas of expertise. For a 20-person business, managed IT support could cost approximately $36,000 to $60,000 per year, depending on the service level. A Simple Comparison Cost Factor In-House IT Outsourced IT Salary Significant annual cost Included in service fee Superannuation Additional Included in provider cost Annual leave Business absorbs coverage gap Provider manages coverage Sick leave Business absorbs coverage gap Provider maintains support Cybersecurity expertise Depends on employee Access to specialist team Networking expertise Depends on employee Access to broader expertise Cloud expertise Depends on employee Access to broader expertise After-hours coverage Usually additional May be included Recruitment Business responsibility Provider responsibility Training Business responsibility Provider responsibility Scalability Hiring required Increase/decrease service as needed For many businesses below around 50 employees, outsourcing can therefore be considerably more cost-effective than building a complete internal IT function. But the financial benefit is only part of the equation. You are also buying depth of expertise, business continuity and access to multiple specialists. When does hiring in-house make more sense? Outsourcing is not automatically the right choice for every business. An internal IT employee or team may make sense when: You have a larger workforce Once your business reaches a certain scale, there may be enough daily IT work to justify dedicated internal staff. You have highly specialised systems Businesses with proprietary platforms, highly customised infrastructure or complex internal systems may benefit from having someone embedded in the organisation. IT is strategically central to the business If technology is directly connected to your core product or operations, an internal technology team may have an important strategic role. You already have an IT employee In this situation, completely replacing internal IT may not be necessary. A co-managed IT model can combine an internal IT person with an external provider. The internal employee handles day-to-day business needs, while the external provider provides additional cybersecurity expertise, specialist support, monitoring, projects and after-hours coverage. For growing businesses, this can provide a practical middle ground. What changes the cost of outsourced IT support? Two businesses with the same number of employees can receive very different IT support quotes. What Is Included in the Package? This is one of the biggest differences between providers. Check whether your monthly fee includes: A lower monthly price can look attractive until you discover that several important services are billed separately. What Hidden IT Support Costs Should You Watch For? The base plan is not always the whole bill. Common extras to ask about: Ask your provider to put every potential additional charge in writing before you sign. How to Compare IT Support Quotes Properly? Any provider who cannot answer those three questions clearly in writing should be ruled out. Byteway Expert Insight When small businesses around Melbourne ask us for a price, what they really want is to compare us against hiring someone. So we put the honest numbers side by side. One in-house hire is six figures a year for a single person who cannot cover every skill or every hour. Outsourced support is a fraction of that for a whole team. For a business under about fifty staff, the maths almost always favours outsourcing,

how to choose a managed network provider
Uncategorized

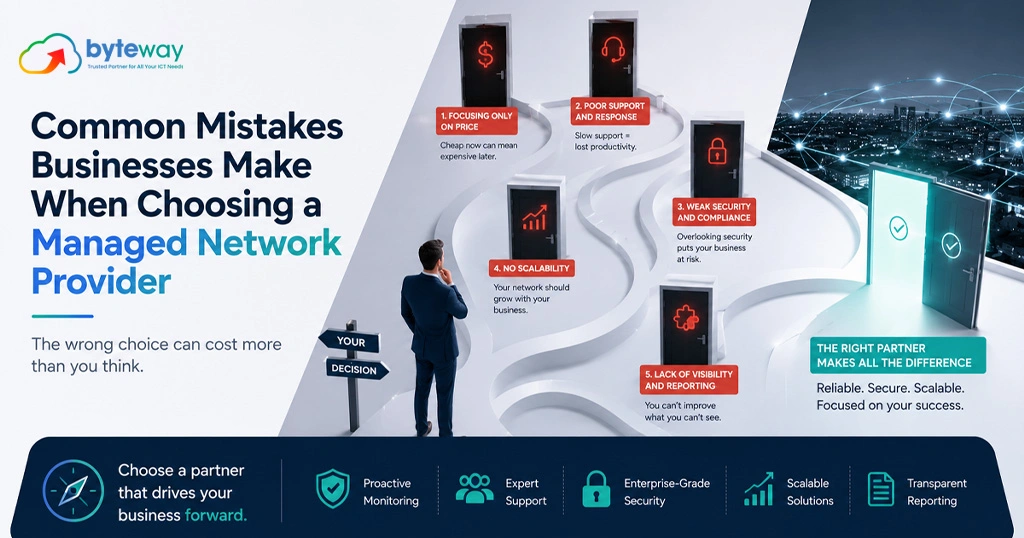
Common Mistakes Businesses Make When Choosing a Managed Network Provider

Byteway is a managed network and IT provider for Australian businesses, and we spend a surprising amount of time helping companies recover from the last provider they chose. Picking the wrong one is an expensive mistake and a painful one to unwind, because by the time the problems show, the provider holds your systems, your passwords and your documentation. This guide covers the common mistakes businesses make when choosing a managed network provider, so you can avoid them and choose a partner you will not need to escape. The short version, before the detail: the biggest mistakes are choosing on price alone, not checking response times and service guarantees, ignoring security, signing into lock-in contracts with no clean exit, and hiring a reactive break-fix operator dressed up as a managed provider. The right choice comes down to a provider who responds fast, works proactively, secures your network, explains what is included in plain terms, lets you keep control of your own systems, and can grow with you. Choose for the day something breaks, not just the day you sign. Why this choice matters more than it looks? A managed network provider does not just fix things. They hold the keys to your business: your network, your data, your access, your documentation. When the relationship is good, you barely think about IT. When it is bad, you are stuck, because the pain of staying is matched by the difficulty of leaving. That is exactly why the choice deserves real scrutiny up front, and why the mistakes below are worth avoiding before you sign, not after. The Common Mistakes Mistake 1: Choosing on price alone The cheapest quote is cheap for a reason, usually thinner support, slower response, less security, or scope gaps that become surprise bills later. IT and network management is not where you want the lowest bidder, because the cost of an outage, a breach or slow support dwarfs the monthly saving. Compare value and what is actually included, not just the headline number. Mistake 2: Not checking response times and guarantees When your network goes down, the only thing that matters is how fast someone fixes it. Many businesses never ask. Before signing, find out the provider’s response and resolution times, whether they are guaranteed, and what happens outside business hours. A great price with a two-day response is not a great deal when you are offline. Mistake 3: Accepting a vague or missing service agreement A proper managed provider gives you a clear service level agreement, response times, what is covered, what is not, and what you can expect. Vague promises like “we’ll look after you” are not commitments. If it is not written down, it is not guaranteed. Ambiguity in the agreement becomes an argument at the worst possible moment. Mistake 4: Ignoring security capability Your network and your security are one job, not two. A provider who manages your network but is weak on cyber security leaves the most important gap open. Ask what they do for security, multi-factor authentication, backups, monitoring, patching, and how they would handle a breach. In a year of record breaches, this is not optional. Mistake 5: Signing into lock-in with no clean exit Some providers make leaving deliberately hard: long contracts, your documentation kept in their heads, your systems configured so only they understand them. Before signing, ask what happens if you leave, do you own your data, your licences, your documentation, and how a handover would work. A confident provider has no problem with a fair exit. One who resists is telling you something. Mistake 6: Hiring reactive break-fix dressed up as “managed” “Managed” should mean proactive: monitoring your systems, catching problems before they cause outages, keeping things patched and maintained. Some providers simply wait for you to call when something breaks and label it managed. Ask what they do when nothing is broken. If the answer is “nothing,” you are buying break-fix with a nicer name. Mistake 7: No proactive monitoring Related, but worth its own point. A real managed provider watches your network and systems continuously, so a failing server, a security alert or a capacity problem is caught early. Without monitoring, your provider finds out something is wrong the same way you do, when it stops working. Mistake 8: Poor communication and no real point of contact If you cannot get a clear answer, a named contact, or a straight explanation without jargon during the sales process, it will be worse once you have signed. Good providers communicate clearly and treat you as a partner. Test this before committing; the sales experience is the best version you will get. Mistake 9: Not checking track record or references Businesses that would check references for any other major supplier skip it for IT. Ask for references, look at how long they have kept clients, and check they have genuine experience with businesses like yours. A provider who cannot point to happy long-term clients is a risk. Mistake 10: Forgetting scalability and your whole environment The provider that suits you now needs to handle where you are going, more staff, more sites, more complexity. And your network does not live in isolation; it connects to your internet, your phones and your other systems. A provider who only sees one piece can leave the seams unmanaged, which is where problems live. Mistake 11: Overlooking the value of one provider for network, internet and phones Many businesses end up with a different supplier for IT, another for internet, another for phones, and spend their time refereeing between them when something goes wrong and each blames the others. A provider who can manage the network, the business internet and the phones together removes that finger-pointing and gives you one accountable partner. This joined-up model is a genuine advantage worth weighing. How to choose well? Run any provider against a simple test: do they respond fast with guaranteed times, work proactively rather than waiting for failures, take security seriously, explain what

Scroll to Top